For some reason, Windows Paint has a remote code execution vulnerability.
It has been revealed that the drawing software '
CVE Record: CVE-2026-83844
https://www.cve.org/CVERecord?id=CVE-2026-83844
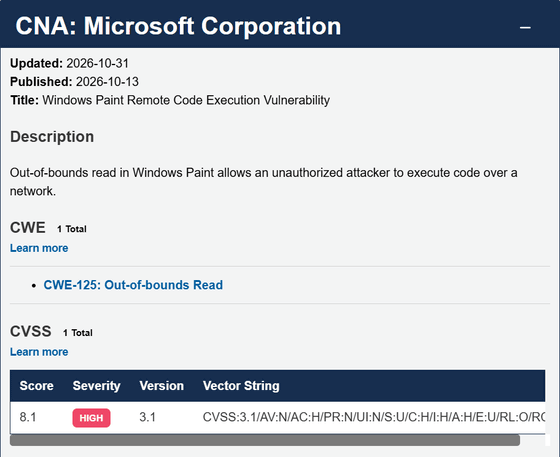
CVE-2026-83844 - Security Update Guide - Microsoft - Windows Paint Remote Code Execution Vulnerability
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-83844
A remote code execution vulnerability has been discovered in Microsoft Paint, the drawing software developed by Microsoft. The CVE number is 'CVE-2026-83844,' with a score of '8.1' and a severity level of 'High.' Versions 11.0.0.0 through 11.2605.91.0 may be affected. The latest affected version of Paint, 11.2605.91.0, was released on June 12, 2026.
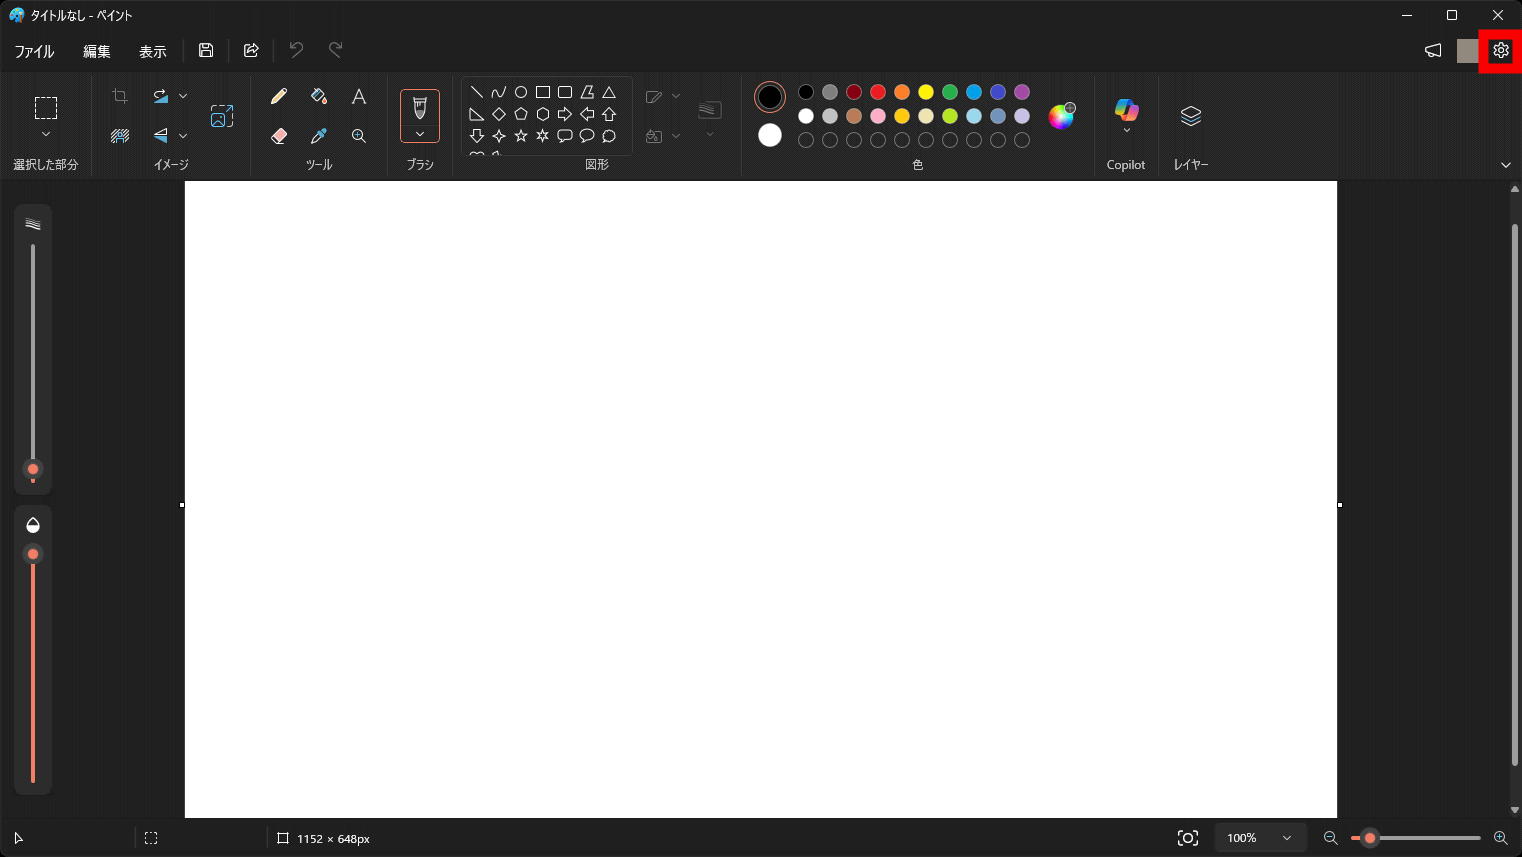
To check the version of Paint you're using, click the gear icon in the upper right corner of the screen.
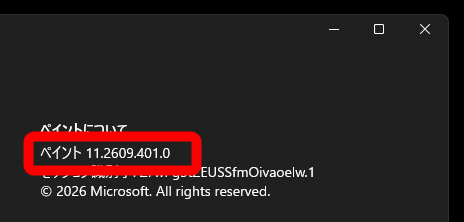
Then, the version will be displayed in the area highlighted in red.
The vulnerability lies in Paint's '
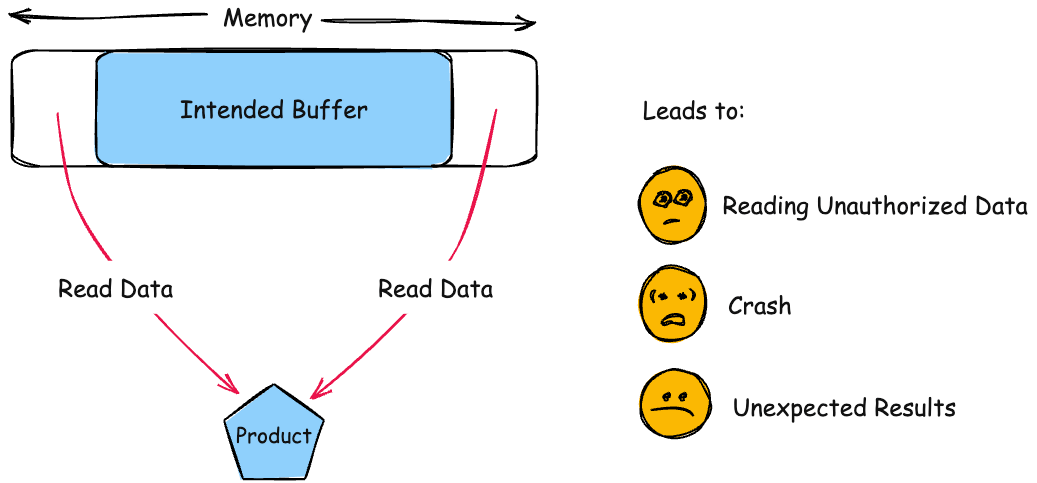
Exploiting this vulnerability could allow an unauthorized attacker to execute code over the network.
On the social forum Hacker News , there were comments such as, 'I had to go to the Microsoft Store to get the fix. Nothing was shown in Windows Update,' and 'If Microsoft knew that it would encourage users to use the app store, they would have created the vulnerability themselves.'
Other comments included, 'I usually delete annoying things like OneDrive, but I left Paint as is because I thought it was harmless,' and 'I'm surprised that Paint is on version 11, let alone 11.2605. I can't even remember the last time I used it.'
Furthermore, there was a comment that said, 'Why on earth does Paint have remote code execution capabilities? Did someone who needed to create a resume decide to do something over the network? The description says that 'an unauthenticated attacker could exploit this vulnerability by sending specially crafted packets to the affected service over the network,' but I don't see how Paint would be friendly to an attacker and cause cryptographic secrets to be leaked. It says sending specially crafted packets , which I suppose means Windows is part of the attack vector, but it just makes the question 'why' bigger. Seriously, why?'
MS Paint Remote Code Execution Vulnerability | Hacker News
https://news.ycombinator.com/item?id=50384233
Related Posts: