It has been discovered that DNA test files used in criminal investigations can be 'undetectable tampered with.'
DNA is crucial information used as evidence in crimes. However, it has been discovered that DNA testing equipment manufactured by Thermo Fisher Scientific has a vulnerability that allows for the falsification of DNA test results. Detecting tampered files is reportedly impossible.
Exclusive | Security Flaw Placed 30 Years of DNA Evidence at Risk of Hacking - WSJ
https://www.wsj.com/tech/cybersecurity/security-flaw-placed-30-years-of-dna-evidence-at-risk-of-hacking-1932775a
According to a report by the Wall Street Journal, the vulnerability in Thermo Fisher Scientific's DNA testing equipment was discovered by Nathan Adams, an engineer at the DNA testing company Forensic Bioinformatics .
Adams successfully used Claude to tamper with DNA test result files included in a 'dataset of publicly available DNA files.' Specifically, he was able to 'combine two DNA test results to create a new DNA test result.' This result file could be tricked into believing that it 'had not been changed at all since 2025,' and it could be read without any problems by DNA analysis software.
Adams reported the vulnerability to Thermo Fisher Scientific in May 2026. Thermo Fisher Scientific publicly acknowledged the vulnerability on July 31, 2026, and provided users with security updates.
Security Bulletin | Thermo Fisher Scientific
(PDF file) https://documents.thermofisher.com/TFS-Assets/CORP/Product-Guides/fsa_hid_bulletin.pdf
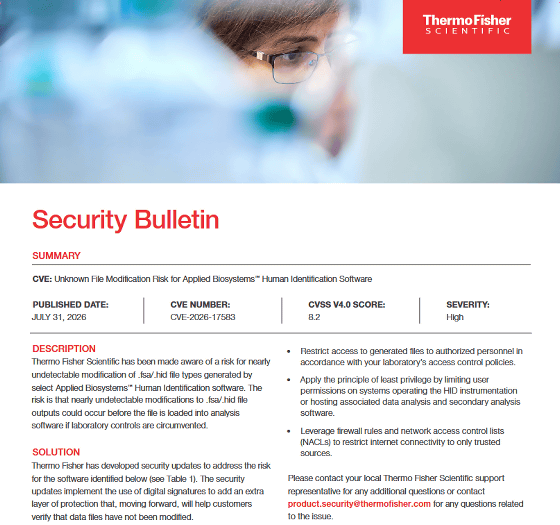
Thermo Fisher Scientific recommends the following measures for users who are unable to apply the update: 'Save files generated by your testing equipment to encrypted storage,' 'Restrict access rights to files,' and 'Review your firewall settings to restrict internet connections to only trusted sources.'
Related Posts:
in Security, Posted by log1o_hf